

A wave of cyberattacks disrupting refrigeration equipment at French supermarkets has expanded beyond a single manufacturer, with authorities confirming that systems supplied by Copeland and Dixell have also been compromised. The incidents have raised concerns about the security of internet-connected industrial equipment used to preserve food.
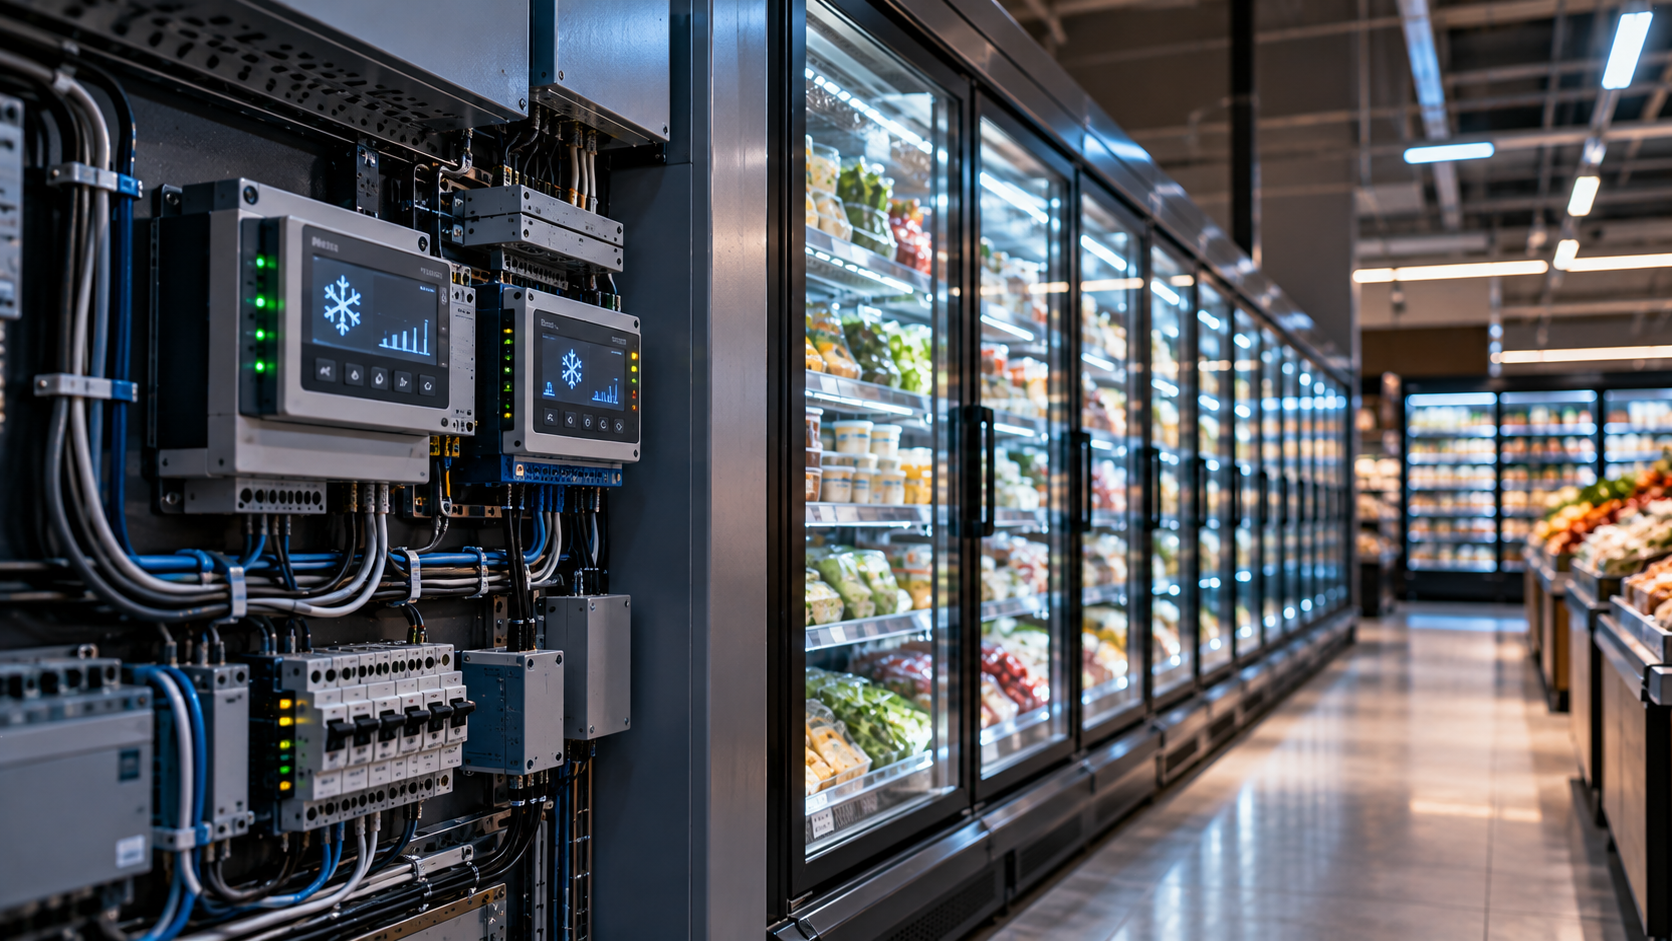
The latest attacks emerged on October 13, 2026, following an earlier operation targeting Danfoss refrigeration controllers at hundreds of supermarkets. Hackers remotely altered cooling settings, causing refrigerators and freezers to overheat, spoiling food and reportedly triggering fires at some locations.
An E.Leclerc supermarket near Albi in southern France was among the newly identified victims. Store director Yoan Rivera reported that employees discovered the incident around 4 a.m., when refrigeration control computers stopped responding normally. The store used Dixell equipment rather than the Danfoss systems implicated in the initial attacks.
Dixell belongs to US-based industrial technology manufacturer Copeland. France’s national cybersecurity agency, ANSSI, subsequently confirmed compromises involving Copeland XWEB and Dixell XWEB refrigeration controllers.
Copeland acknowledged a security vulnerability affecting an older, discontinued generation of controllers and said it was assisting affected customers. However, the company did not confirm that this particular weakness was responsible for the attacks.
Security specialists believe the incidents highlight a broader problem involving industrial controllers exposed directly to the internet. These devices enable maintenance contractors to monitor temperatures and adjust refrigeration settings remotely, but inadequate protection can also make them accessible to attackers.
Cybersecurity company SOCRadar reported finding nearly 2,900 internet-accessible Danfoss systems in France during an October 13 scan. That represented approximately 65% of the roughly 4,500 exposed systems identified worldwide, although internet exposure alone does not establish that a device has been compromised.
Researchers at Claroty previously disclosed vulnerabilities affecting refrigeration management platforms from Danfoss and Copeland. Some weaknesses could potentially allow unauthorized changes to operational settings, but investigators have not confirmed whether those flaws were exploited in the current campaign.
French cybersecurity authorities have advised operators to remove exposed management interfaces from the public internet, inspect potentially compromised equipment and restore affected controllers securely. They also recommend using protected networks or VPN connections and keeping supported firmware updated.
The Paris prosecutor’s office has opened a criminal investigation into the disruptions and resulting damage. No hacking group has publicly claimed responsibility, and investigators have not established the attackers’ identities or motives.