

ClosedQuorum is a Windows malware program designed to steal sensitive information and give attackers additional control over an infected computer. Its targets include passwords stored in web browsers, login credentials, and data associated with cryptocurrency wallets.
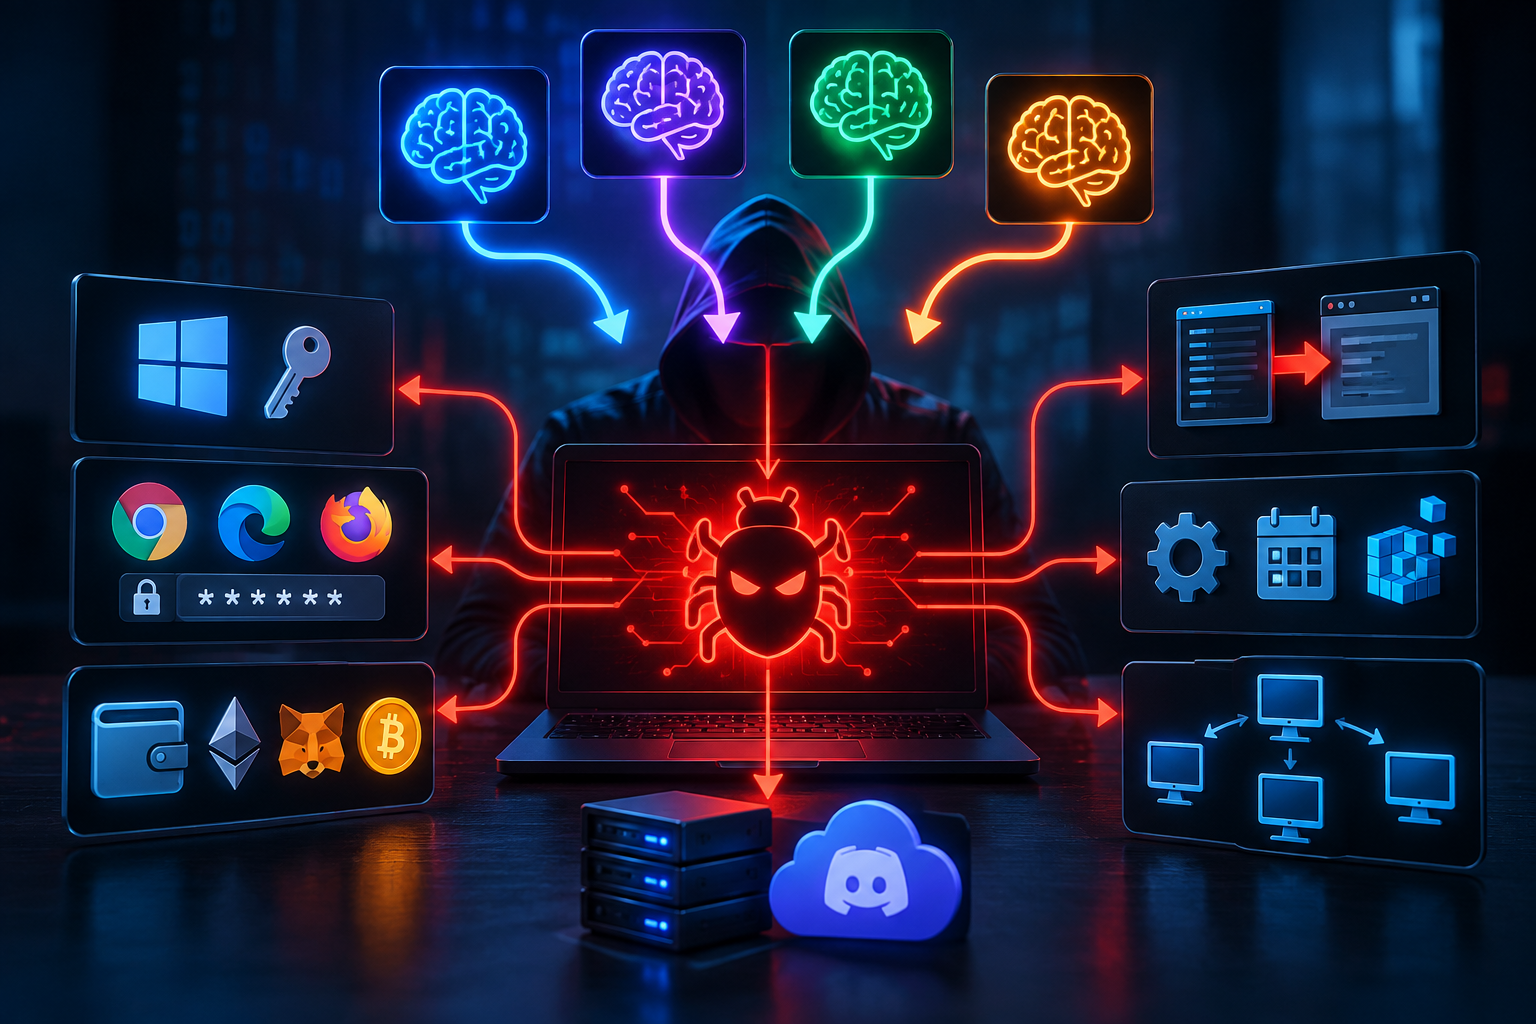
What makes ClosedQuorum unusual is its use of artificial intelligence. Instead of relying entirely on instructions sent by an attacker, the malware can contact several commercial AI services and ask them which malicious action it should perform next.
ClosedQuorum can communicate with DeepSeek, Qwen, Mistral, and Google Gemini. These AI models are given four possible actions to choose from: steal information, inject malicious code into another process, establish persistence, or move to another system on the local network.
The malware compares the answers and follows the option selected by the largest number of models. If the result is tied, DeepSeek is used to make the final decision. The AI services are therefore not creating entirely new attacks. They are choosing between actions that are already built into ClosedQuorum.
One of those actions focuses on stealing information. ClosedQuorum can extract credentials from Windows and collect saved passwords and session information from Chrome, Edge, and Firefox. It can also target cryptocurrency-related data associated with services and extensions such as MetaMask, Exodus, and Ethereum.
Another capability allows ClosedQuorum to hide its malicious activity inside other running processes. It supports techniques known as Early Bird APC injection and process hollowing. In practical terms, these methods allow malicious code to run from within processes that may appear legitimate.
ClosedQuorum can also configure Windows so that it continues operating after the computer is restarted. It can create a Registry Run entry, add a scheduled task, and establish a WMI event subscription. Using several persistence methods can make an infection harder to completely remove.
The malware contains functionality intended to spread to other computers on the same network. However, this feature did not work in the samples that were analyzed. It should therefore not be treated as a confirmed working capability of the examined version.
ClosedQuorum also takes steps to make its activity less noticeable. It can interfere with Event Tracing for Windows, a Windows logging mechanism that can help security tools observe activity. The malware also waits five minutes before taking its first action and later contacts AI services at randomized intervals of between five and fifteen minutes.
Information stolen from an infected computer is encrypted before it is sent to the attackers. ClosedQuorum uses AES-256-GCM encryption, encodes the resulting data, divides it into smaller pieces, and sends it through a Discord webhook.
Overall, ClosedQuorum combines several capabilities normally associated with information stealers and remote access malware. It can steal credentials and cryptocurrency-related information, inject code into other processes, maintain access to an infected computer, and use external AI models to help determine which built-in malicious action to perform next.
How is ClosedQuorum distributed and how can infections be avoided?
The distribution model behind ClosedQuorum is different from its actual delivery method to victims. Customized builds can be produced for criminal operators, with each binary containing operator-specific AI API keys and a Discord webhook address. This gives individual builds their own configuration and exfiltration channel.
However, the specific method used to install ClosedQuorum on victims’ computers has not been confirmed from the analyzed samples. There is currently insufficient evidence to state that a particular phishing campaign, installer, software crack, or malicious website is responsible for delivering it.
Phishing attachments, fake software downloads, deceptive advertisements, pirated programs, activation cracks, and unofficial download services are common ways malware can reach Windows systems, but these should be treated as potential routes rather than confirmed ClosedQuorum distribution methods.
This distinction is particularly important because the examined ClosedQuorum samples contained placeholder credentials. At the time of the analysis, there were also no confirmed reports of these samples being deployed in real-world attacks.
Users can reduce their exposure to malware by treating unexpected email attachments and links cautiously and obtaining programs from official developers or trusted application stores. Pirated software, activation tools, key generators, and downloads from questionable third-party sources should be avoided.
Windows and installed applications should also be kept updated, while reputable security software can help identify malicious files before or after execution. An unexpected executable should not be launched simply because its filename or icon suggests that it belongs to Windows or another trusted product.
Site Disclaimer
2-remove-virus.com is not sponsored, owned, affiliated, or linked to malware developers or distributors that are referenced in this article. The article does not promote or endorse any type of malware. We aim at providing useful information that will help computer users to detect and eliminate the unwanted malicious programs from their computers. This can be done manually by following the instructions presented in the article or automatically by implementing the suggested anti-malware tools.
The article is only meant to be used for educational purposes. If you follow the instructions given in the article, you agree to be contracted by the disclaimer. We do not guarantee that the artcile will present you with a solution that removes the malign threats completely. Malware changes constantly, which is why, in some cases, it may be difficult to clean the computer fully by using only the manual removal instructions.